

If your device’s store shows no 1xBet application, the software remains available through direct download. Regional restrictions on gambling apps mean many users must sideload the program instead of using automatic storefront installation. This approach requires understanding Android’s security architecture and the file format that makes manual installation possible.
What the Application and Its APK Actually Are
A PK file is Android’s package format for distributing mobile software. When developers publish through Google Play, this file arrives hidden behind the store’s interface. Direct distribution exposes this container, which holds compiled code, resources, certificates, and the manifest that tells your phone how the program should behave. The 1xBet release uses this standard mechanism.
The certificate embedded in the package proves who built the software. Android verifies this signature during installation and again during updates. Mismatched certificates between versions block the update process entirely, forcing complete removal and reinstallation that may erase locally stored data such as login sessions or saved preferences.
Sideloaded applications run with the same permissions as store-installed counterparts. The distinction lies in how they reached your device, not in their capabilities. Your phone treats the betting program as it would any other installed software once the package validates successfully.
Obtaining the 1xbet android package for android phones requires identifying a distribution source. The operator maintains regional portals where the current release resides. These pages typically detect your device type and offer the appropriate build automatically.
Getting the Software Onto Your Device
The download process begins in your mobile browser. Navigate to the operator’s mobile portal, where a prominent button initiates file transfer. Your browser saves this to a default location, usually the Downloads folder, unless you have configured alternative storage paths. The file name typically incorporates version indicators.
Before initiating transfer, verify the source carefully. Malicious copies circulate through unofficial channels, sometimes mimicking legitimate branding. Check that the domain matches the operator’s established regional presence. The genuine package carries a valid digital signature that Android can verify during installation.
Connection stability matters during transfer. Interrupted downloads produce corrupted files that fail installation without clear error messages. If the transfer stalls, delete the partial file and restart rather than attempting to resume. A complete, uncorrupted package is essential for the next phase.
Storage requirements vary by release, though betting applications remain relatively compact compared to graphics-intensive games. Ensure adequate free space before beginning. The downloaded file persists after installation and can be deleted manually once the program runs successfully.
Installation and the Unknown-Source Permission
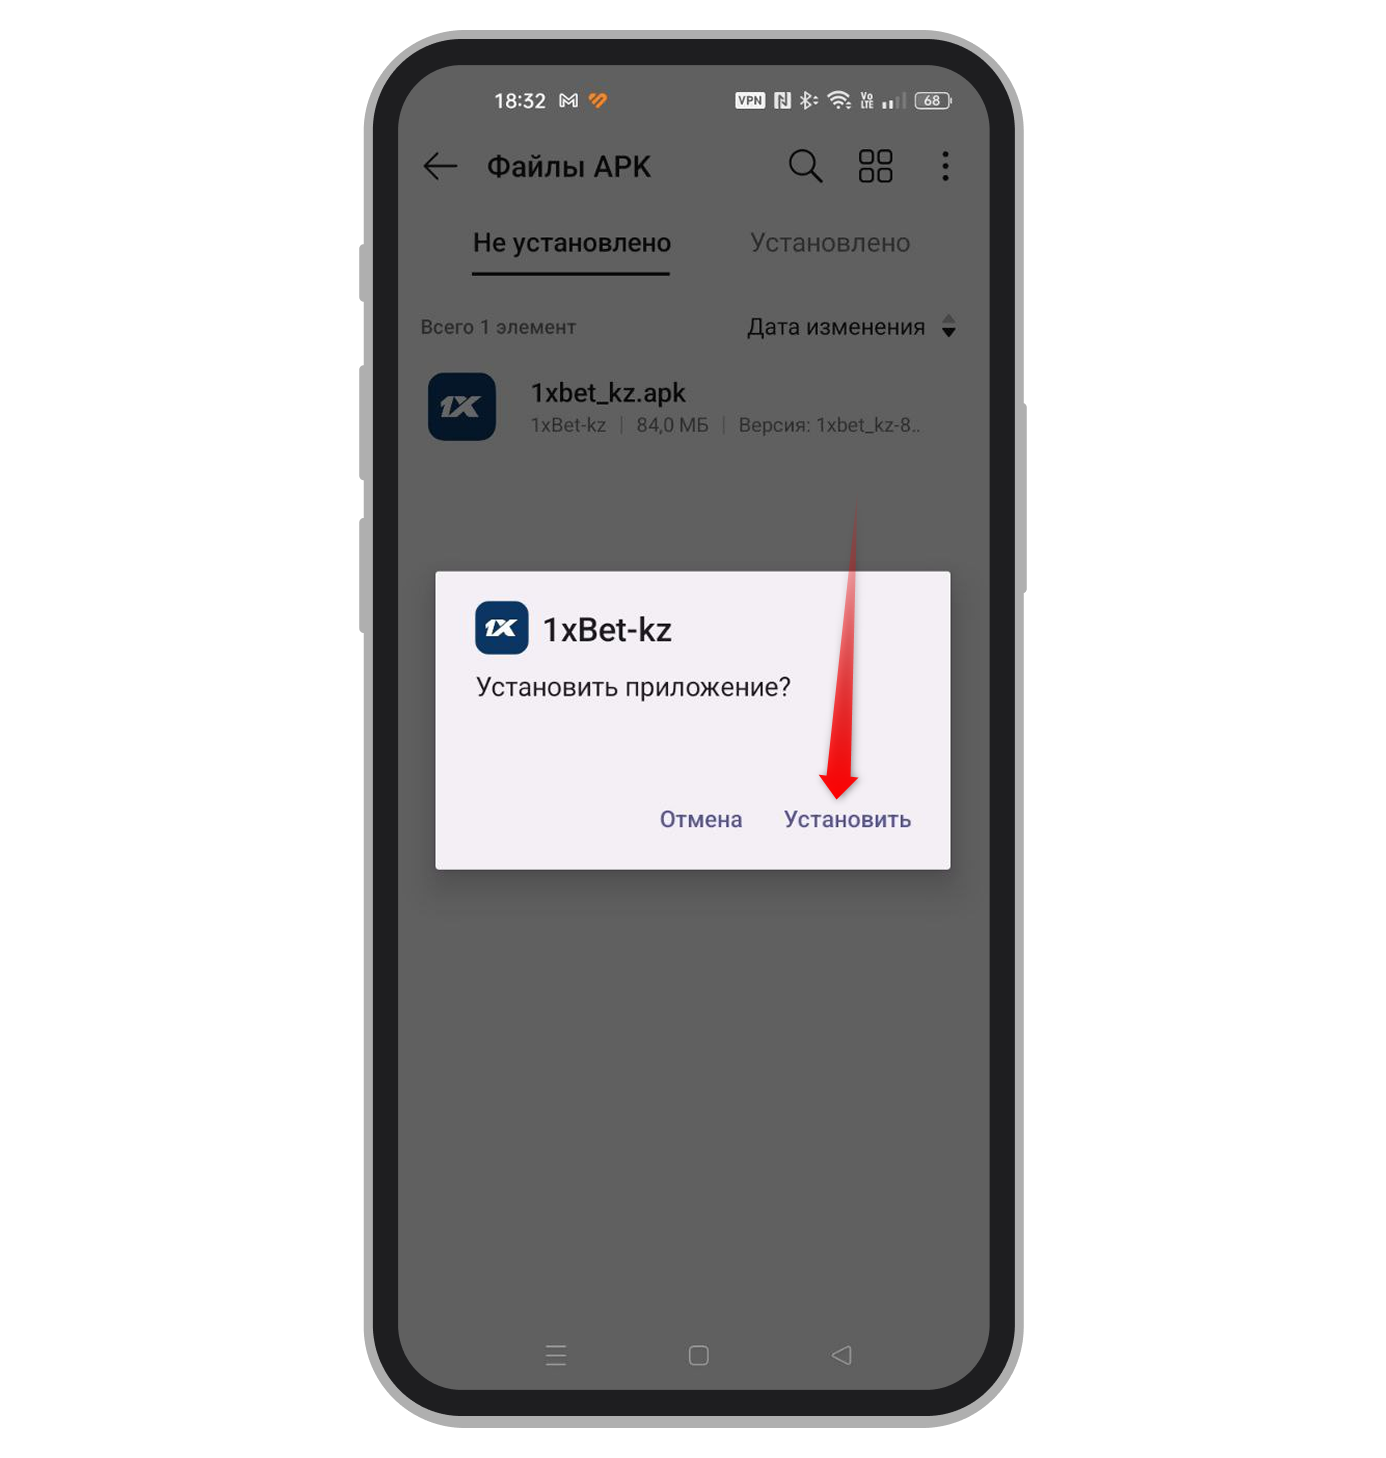
Android’s security model restricts installation from sources other than the pre-installed store. Enabling this capability requires navigating to Settings, then Apps or Applications, then locating the specific app that will handle the installation—typically your browser or file manager. The permission grants that specific program authority to install packages, not a global system-wide exemption.
The permission interface changed significantly across Android versions. Older releases presented a single system-wide toggle in Security settings. Current versions implement per-source authorization, meaning you enable installation specifically for the browser that downloaded the file or the file manager that will open it. This granularity improves security by limiting which programs can modify your software inventory.
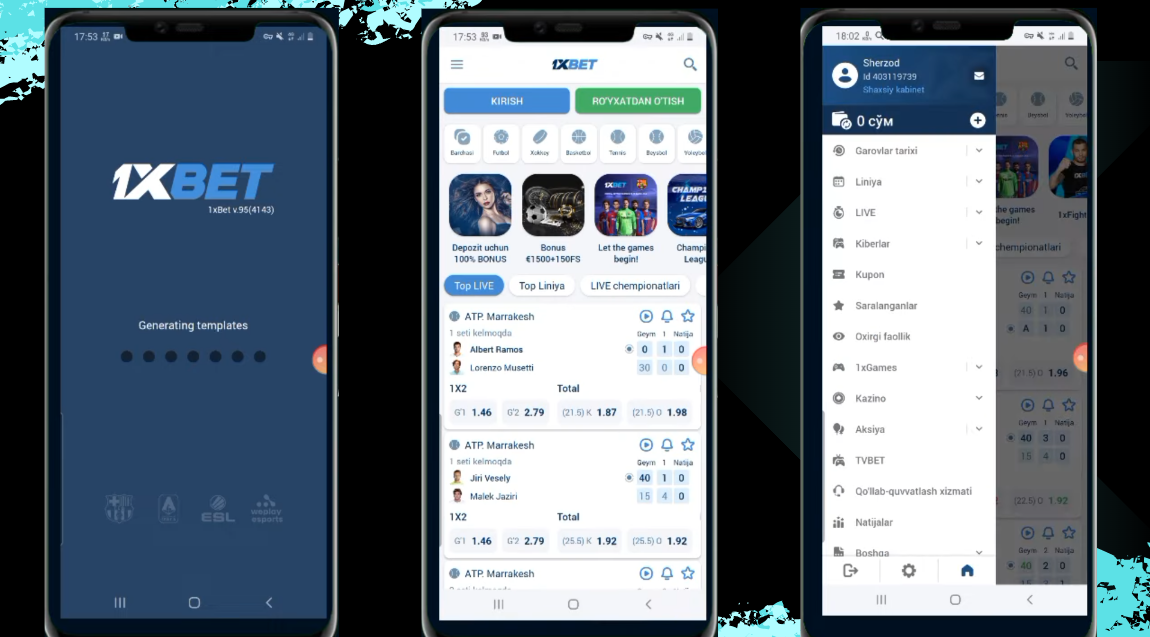
Once permission is active, opening the APK triggers the system installer. A screen displays requested permissions, the signing certificate status, and storage requirements. Proceed only if these details appear consistent with expectations. The process completes within seconds on modern hardware.
Post-installation, the permission can be revoked without affecting the installed program. Return to the same settings location and disable the toggle. The betting software continues functioning normally; only future installations from that specific source are blocked. This cleanup step reduces your device’s attack surface.
| Installation Phase | Critical Action | Common Oversight |
|---|---|---|
| Download | Verify domain authenticity | Resuming interrupted transfers |
| Permission | Enable per-source, not global | Leaving permission active permanently |
| Execution | Check certificate consistency | Ignoring permission warnings |
| Cleanup | Revoke unnecessary permissions | Retaining APK after installation |
Updates, Core Capabilities, and Typical Obstacles
Update mechanics mirror initial installation. The operator releases new builds through the same distribution channels, not through automatic update frameworks. You must manually obtain each new package and install it over the existing version. This overlay preserves account data and preferences when certificates match.
Certificate mismatches produce update failures that appear as generic parsing errors. This occurs if you initially installed from one source and attempt update from another, or if the operator rotated signing keys between releases. The resolution requires complete uninstallation followed by fresh installation, with the acknowledged risk of local data loss.
The software provides comprehensive betting functionality: pre-match wagering across sporting categories, live betting with fluctuating odds during events, casino games with varying mechanics, and financial transaction processing. Account management including deposits, withdrawals, and documentation submission operates within the same interface. Notification delivery for match results or promotional offers depends on push notifications being enabled at system level.
Several predictable issues arise during adoption:
- Parse errors indicate corrupted downloads or version incompatibility; re-download completely
- Blocked installation points to missing or misconfigured source permissions; verify the specific app granted authority
- Application crashes on launch suggest insufficient resources or conflicts with security software; attempt restart or temporary disabling of scanning tools
- Login failures typically stem from regional restrictions or account verification requirements rather than technical malfunction
- Slow performance during live betting reflects network latency or server load rather than local software deficiency
Responsible gambling tools reside within account settings, allowing deposit limits, cooling-off periods, and self-exclusion activation. These function identically across application and website interfaces.
| Problem Symptom | Underlying Cause | Resolution Approach |
|---|---|---|
| Package blocked | Source permission disabled | Re-enable per-app installation right |
| Update incompatible | Certificate mismatch | Backup data, uninstall, reinstall fresh |
| Odds not loading | Regional server routing | Verify account jurisdiction matches |
| Payment declined | Method restriction or limit | Review account verification status |

The mobile website presents a viable alternative requiring no installation. Browser-based access eliminates certificate concerns, update management, and permission complications. Performance depends on browser efficiency rather than native optimization, and certain features may load progressively rather than residing immediately accessible.
Installed software offers marginally faster startup, offline browsing of cached content, and more reliable notification delivery. The website requires no storage commitment and functions across devices immediately. Both access methods connect to identical account infrastructure and betting pools. Regional availability and interface presentation vary by jurisdiction and connection point regardless of access method chosen.

FAQ
Why does the permission requirement exist for this specific app?
Android’s security model treats all non-store software uniformly. The restriction protects against unintended installation of potentially harmful code. Gambling applications frequently face store policy exclusions, making sideloading necessary regardless of the developer’s legitimacy. The permission mechanism ensures you consciously authorize each installation source.
What actually happens if I ignore an available update?
The existing installation continues functioning until server-side changes render it incompatible. Older versions may lose access to new features, encounter display errors, or fail authentication checks. Critical security patches arrive only through updated packages. Delaying update risks service interruption without warning when compatibility thresholds are enforced.
How do I confirm my downloaded file matches the operator’s release?
Android’s installer performs signature verification automatically, rejecting tampered packages. Visual confirmation of file size consistency with published expectations provides secondary assurance. The operator’s download pages typically display version identifiers you can cross-reference after transfer completes. No manual cryptographic verification is required for standard use.
Does switching between app and website affect my betting history or funds?
Account data resides on operator servers, not local device storage. Wagers, balances, and history appear identically across access methods. Session-specific elements like partially completed betslips may not synchronize in real-time between platforms. Completed transactions and settled bets maintain permanent records accessible universally.
Why might the same installation steps succeed on one device but fail on another?
Manufacturer Android modifications alter permission interfaces and security behaviors. Corporate device management policies can override user-granted installation rights. Pre-installed security software may intercept APK handling with proprietary scanning that rejects legitimate packages. Regional network restrictions sometimes intercept downloads, delivering placeholder files instead of genuine packages.
